# Wireguard Client & iptables
**URL:** https://dietpi.com/forum/t/wireguard-client-iptables/13356
**Category:** Troubleshooting
**Created:** [7 June 2022 19:16 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356 "2022-06-07T19:16:12Z")
**Posts on this page:** 20
**Page:** 1
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [7 June 2022 19:16 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/1 "2022-06-07T19:16:12Z")
Thought it might be easier to create a new topic, instead of using an old guide: [this one](https://dietpi.com/forum/t/guide-very-basic-wireguard-mullvad-qbittorrent-external-storage-pi-hole-and-rpi-monitor-setup/3481).
#### Basic information
DietPi version:
> G\_DIETPI\_VERSION\_CORE=8
> G\_DIETPI\_VERSION\_SUB=5
> G\_DIETPI\_VERSION\_RC=1
> G\_GITBRANCH=‘master’
> G\_GITOWNER=‘MichaIng’
Distro version:
> bullseye 0
Kernel version:
> Linux DietPi 5.15.32-v8+ #1538 SMP PREEMPT Thu Mar 31 19:40:39 BST 2022 aarch64 GNU/Linux
SBC model:
> RPi 3 Model B (aarch64)
Power supply used: 5V 2A
SD card used: Samsung FIT 32GB
#### Additional Information
- Software: Wireguard Client
- Freshly installed DietPi and Wireguard client
#### Steps to reproduce
1. New Dietpi installation. (Fresh, basic, OpenSSH, changed CPU setting and timezone)
2. Installed WireGuard as a client
3. Created a conf file on the Mullvad website: tunnel traffic: Only IPv4, No Killswitch, block all content
4. Created /etc/wireguard/mullvad.conf
5. Copied Mullvad conf file to mullvad.conf:
> [Interface]
> PrivateKey = PrKey
> Address = 10.64.56.12/32
> DNS = Local IP Pi-Hole
> [Peer]
> PublicKey = PuKEY
> AllowedIPs = 0.0.0.0/0
> Endpoint = 185.254.75.3:51820
1. Started WireGuard (wg-quick up mulvad.conf )
2. Checked VPN connection: OK (curl [ifconfig.me](http://ifconfig.me) && curl [https://am.i.mullvad.net/connected](https://am.i.mullvad.net/connected))
3. Added it to start up: systemctl enable wg-quick@mullvad
4. Reboot: all OK
5. Added a killswitch command to mullvad.conf (used it from [here:mullvad](https://mullvad.net/nl/help/wireguard-and-mullvad-vpn/))
> [Interface]
> PrivateKey = Key
> Address = 10.64.56.12/32
> DNS = IP adress Pi-Hole
> PostUp = iptables -I OUTPUT ! -o %i -m mark ! --mark $(wg show
> %i fwmark) -m addrtype ! --dst-type LOCAL -j REJECT && ip6tables
> -I OUTPUT ! -o %i -m mark ! --mark $(wg show %i fwmark) -m addrtype !
> –dst-type LOCAL -j REJECT
> PreDown = iptables -D OUTPUT ! -o %i -m mark ! --mark $(wg show %i
> fwmark) -m addrtype ! --dst-type LOCAL -j REJECT && ip6tables -D
> OUTPUT ! -o %i -m mark ! --mark $(wg show %i fwmark) -m addrtype !
> –dst-type LOCAL -j REJECT
> [Peer]
> PublicKey = KEY
> AllowedIPs = 0.0.0.0/0
> Endpoint = 185.254.75.3:51820
1. Reboot: Pi unreabable
2. ps Pi also unreachable after only adding this:
> [Interface]
> PrivateKey = KEY
> Address = 10.64.56.12/32
> DNS = IP adress Pi-Hole
> PostUp = iptables -I OUTPUT ! -o %i -m mark ! --mark $(wg show
> %i fwmark) -m addrtype ! --dst-type LOCAL -j REJECT
> [Peer]
> PublicKey = KEY
> AllowedIPs = 0.0.0.0/0
> Endpoint = 185.254.75.3:51820
#### Expected behaviour
- Pi makes a VPN connection
- Still be able to connect to the Pi (SSH)
- Killswitch when VPN is offline. (No connection out and Transmission-deamon killed)
- No IPv6 leaking
#### Actual behaviour
- Pi unreachable, but still showing up in network
#### Extra details
I have read on serveral sites about Wireguard & iptables (most are about setting up WG servers):
- [How To Implement a Basic Firewall Template with Iptables on Ubuntu 20.04 | DigitalOcean](https://www.digitalocean.com/community/tutorials/how-to-implement-a-basic-firewall-template-with-iptables-on-ubuntu-20-04)
- [Iptables Essentials: Common Firewall Rules and Commands | DigitalOcean](https://www.digitalocean.com/community/tutorials/iptables-essentials-common-firewall-rules-and-commands)
- [https://www.cyberciti.biz/faq/how-to-set-up-wireguard-firewall-rules-in-linux/](https://www.cyberciti.biz/faq/how-to-set-up-wireguard-firewall-rules-in-linux/)
- [https://medium.com/tangram-visions/what-they-dont-tell-you-about-setting-up-a-wireguard-vpn-46f7bd168478](https://medium.com/tangram-visions/what-they-dont-tell-you-about-setting-up-a-wireguard-vpn-46f7bd168478)
- [Wireguard and iptables restrictions for multiple users · GitHub](https://gist.github.com/qdm12/4e0e4f9d1a34db9cf63ebb0997827d0d)
This is another step in learning more about iptables and network in generally.
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [7 June 2022 19:59 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/2 "2022-06-07T19:59:00Z")
If i only execute the first iptable line, after VPN is running (step 5):
> iptables -I OUTPUT ! -o %i -m mark ! --mark $(wg show %i fwmark) -m addrtype ! --dst-type LOCAL -j REJECT
I get this message:
_Unable to access interface: No such device_
_iptables v1.8.7 (nf\_tables): mark: bad integer value for option “–mark”, or out of range._
---
### Author:  [@Joulinar](https://dietpi.com/forum/u/Joulinar)
#### Post date: [7 June 2022 20:12 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/3 "2022-06-07T20:12:03Z")
yes because the code line is working inside wireguard config file only as you have a variable `%i`. This one you need to set manually if you go to execute the code line yourself. Usually it should be `wg0`.
---
### Author:  [@MichaIng](https://dietpi.com/forum/u/MichaIng)
#### Post date: [8 June 2022 06:12 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/4 "2022-06-08T06:12:11Z")
The rules block any outgoing packets that are not tunnelled, hence the Pi isn’t able to answer on any SSH request. You need to add an additional rule to explicitly permit all outgoing SSH packets, or those to your LAN at least.
The `LOCAL` doesn’t mean LAN here, but loopback/localhost destination only, AFAIK.
---
### Author:  [@trendy](https://dietpi.com/forum/u/trendy)
#### Post date: [8 June 2022 09:38 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/5 "2022-06-08T09:38:56Z")
You need to add a rule to allow ssh and anything else you need to the dietpi.
`iptables -I INPUT -i eth0 -p tcp -s 192.168.0.0/24 --dport 22 -j ACCEPT; iptables -I OUTPUT -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT`
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [8 June 2022 18:39 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/6 "2022-06-08T18:39:42Z")
Do I need to add these lines to the mullvad.conf in PostUp?
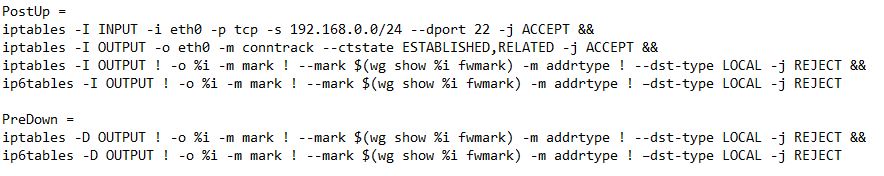
Or do I add them as persistant iptables?
---
### Author:  [@Joulinar](https://dietpi.com/forum/u/Joulinar)
#### Post date: [8 June 2022 18:49 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/7 "2022-06-08T18:49:20Z")
you can add it into PustUp part and to revert into PostDown.
BTW: there is no need to do screen prints. You could copy everything from SSH terminal directly 😜
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [8 June 2022 18:53 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/8 "2022-06-08T18:53:51Z")
Hehe, I don’t have the chance to add it into the confi file yet.
Just wanted to make sure I put it in the right place when I can add it.
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [8 June 2022 19:10 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/9 "2022-06-08T19:10:19Z")
I first added only Trendy’s rule and it was fine:
> PostUp = `iptables -I INPUT -i eth0 -p tcp -s 192.168.1.0/24 --dport 22 -j ACCEPT && iptables -I OUTPUT -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT`
> PostDown = `iptables -I INPUT -i eth0 -p tcp -s 192.168.1.0/24 --dport 22 -j ACCEPT && iptables -I OUTPUT -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT`
But the Pi became unreachable after adding this:
> PostUp = `iptables -I INPUT -i eth0 -p tcp -s 192.168.1.0/24 --dport 22 -j ACCEPT && iptables -I OUTPUT -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT && iptables -I OUTPUT ! -o %i -m mark ! --mark $(wg show %i fwmark) -m addrtype ! --dst-type LOCAL -j REJECT`
> PostDown = `iptables -I INPUT -i eth0 -p tcp -s 192.168.1.0/24 --dport 22 -j ACCEPT && iptables -I OUTPUT -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT`
ps I changed the IP adress because this computer and the Pi use IP range 192.168.1.XXX
---
### Author:  [@trendy](https://dietpi.com/forum/u/trendy)
#### Post date: [9 June 2022 08:46 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/10 "2022-06-09T08:46:38Z")
Do it like this:
```auto
PostUp = `iptables -I 1 INPUT -i eth0 -p tcp -s 192.168.1.0/24 --dport 22 -j ACCEPT && iptables -I 1 OUTPUT -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT && iptables -I 2 OUTPUT ! -o %i -m mark ! --mark $(wg show %i fwmark) -m addrtype ! --dst-type LOCAL -j REJECT`
PostDown = `iptables -D INPUT -i eth0 -p tcp -s 192.168.1.0/24 --dport 22 -j ACCEPT && iptables -D OUTPUT -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT && iptables -D OUTPUT ! -o %i -m mark ! --mark $(wg show %i fwmark) -m addrtype ! --dst-type LOCAL -j REJECT`
```
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [11 June 2022 11:55 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/11 "2022-06-11T11:55:31Z")
When I add these lines to the conf file, without rebooting, I get this message:
> root@DietPi:/etc/wireguard# wg-quick up mullvad-de21.conf
> [#] ip link add mullvad-de21 type wireguard
> [#] wg setconf mullvad-de21 /dev/fd/63
> [#] ip -4 address add 10.65.134.216/32 dev mullvad-de21
> [#] ip link set mtu 1420 up dev mullvad-de21
> [#] resolvconf -a tun.mullvad-de21 -m 0 -x
> [#] wg set mullvad-de21 fwmark 51820
> [#] ip -4 route add 0.0.0.0/0 dev mullvad-de21 table 51820
> [#] ip -4 rule add not fwmark 51820 table 51820
> [#] ip -4 rule add table main suppress\_prefixlength 0
> [#] sysctl -q net.ipv4.conf.all.src\_valid\_mark=1
> [#] iptables-restore -n
> [#] iptables -I 1 INPUT -i eth0 -p tcp -s 192.168.1.0/24 --dport 22 -j ACCEPT && iptables -I 1 OUTPUT -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT && iptables -I 2 OUTPUT ! -o mullvad-de21 -m mark ! --mark $(wg show mullvad-de21 fwmark) -m addrtype ! --dst-type LOCAL -j REJECT
> iptables v1.8.7 (nf\_tables): Invalid rule number `INPUT' Try `iptables -h’ or ‘iptables --help’ for more information.
> [#] resolvconf -d tun.mullvad-de21 -f
> [#] iptables-restore -n
> [#] ip -4 rule delete table 51820
> [#] ip -4 rule delete table main suppress\_prefixlength 0
> [#] ip link delete dev mullvad-de21
---
### Author:  [@Joulinar](https://dietpi.com/forum/u/Joulinar)
#### Post date: [11 June 2022 12:03 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/12 "2022-06-11T12:03:59Z")
> [@Xperimental](#):
>
> iptables -I 1 INPUT
I guess the `INPUT` rule #1 already exist and can’t be set again.
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [11 June 2022 12:17 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/13 "2022-06-11T12:17:39Z")
Can it be fixed by replacing rule #1 with #2 and rule #2 with #3?
Or do we need to change more stuff?
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [11 June 2022 12:27 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/15 "2022-06-11T12:27:07Z")
> root@DietPi:/etc/wireguard# sudo iptables -S INPUT
> -P INPUT ACCEPT
There aren’t any rules listed. Nothing is listed when I use the command “sudo iptables -S”
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [11 June 2022 12:56 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/18 "2022-06-11T12:56:42Z")
I placed the numbers behind INPUT / OUTPUT, that solved the issue.
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [11 June 2022 13:39 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/19 "2022-06-11T13:39:17Z")
When I kill wireguard, this happens and I cannot access the pi anymore:
```auto
root@DietPi:/etc/wireguard# wg-quick down mullvad-de21
[#] systemctl stop transmission-daemon
[#] ip -4 rule delete table 51820
[#] ip -4 rule delete table main suppress_prefixlength 0
[#] ip link delete dev mullvad-de21
[#] resolvconf -d tun.mullvad-de21 -f
[#] iptables-restore -n
[#] iptables -D INPUT -i eth0 -p tcp -s 192.168.1.0/24 --dport 22 -j ACCEPT && iptables -D OUTPUT -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT && iptables -D OUTPUT ! -o mullvad-de21 -m mark ! --mark $(wg show mullvad-de21 fwmark) -m addrtype ! --dst-type LOCAL -j REJECT
```
I guess the PostDown needs some adjustments?
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [12 June 2022 09:10 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/20 "2022-06-12T09:10:32Z")
I think I have found the solution:
```auto
PostUp = iptables -I INPUT 1 -i eth0 -p tcp -s 192.168.1.0/24 --dport 22 -j ACCEPT && iptables -I OUTPUT 1 -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT && iptables -I OUTPUT 2 ! -o %i -m mark ! --mark $(wg show %i fwmark) -m addrtype ! --dst-type LOCAL -j REJECT
PreDown = iptables -D INPUT -i eth0 -p tcp -s 192.168.1.0/24 --dport 22 -j ACCEPT && iptables -D OUTPUT -o eth0 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT && iptables -D OUTPUT ! -o %i -m mark ! --mark $(wg show %i fwmark) -m addrtype ! --dst-type LOCAL -j REJECT
```
Changed place numbers and PostDown to PreDown.
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [12 June 2022 20:05 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/21 "2022-06-12T20:05:19Z")
New problem:
I am not able to access files from the NAS anymore. The drive is mounted. Is this because of the IP tables?
---
### Author:  [@Joulinar](https://dietpi.com/forum/u/Joulinar)
#### Post date: [12 June 2022 20:14 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/22 "2022-06-12T20:14:53Z")
yes, because you allowed SSH only while VPN is connected.
---
### Author:  [@Xperimental](https://dietpi.com/forum/u/Xperimental)
#### Post date: [12 June 2022 21:04 UTC](https://dietpi.com/forum/t/wireguard-client-iptables/13356/23 "2022-06-12T21:04:00Z")
Is there a standard NFS port?
[Next page](https://dietpi.com/forum/t/wireguard-client-iptables/13356.md?page=2)